EU CRA · Reporting obligations in effect since 11 September 2026 → full application 11 December 2027
How are you preparing for your CRA obligations?
Reporting obligations · supply-chain security · CRA deliverables — in one place.

How are you handling this today?
An exploited vulnerability comes to light at dawn. Within 24 hours, who does what?
A new vulnerability is disclosed. Who checks whether it affects components in our product?
Documents due by 11 December 2027 — do you have the templates to start from?


This is how CRAdle answers.
Below, we show only what is on the product screens today.
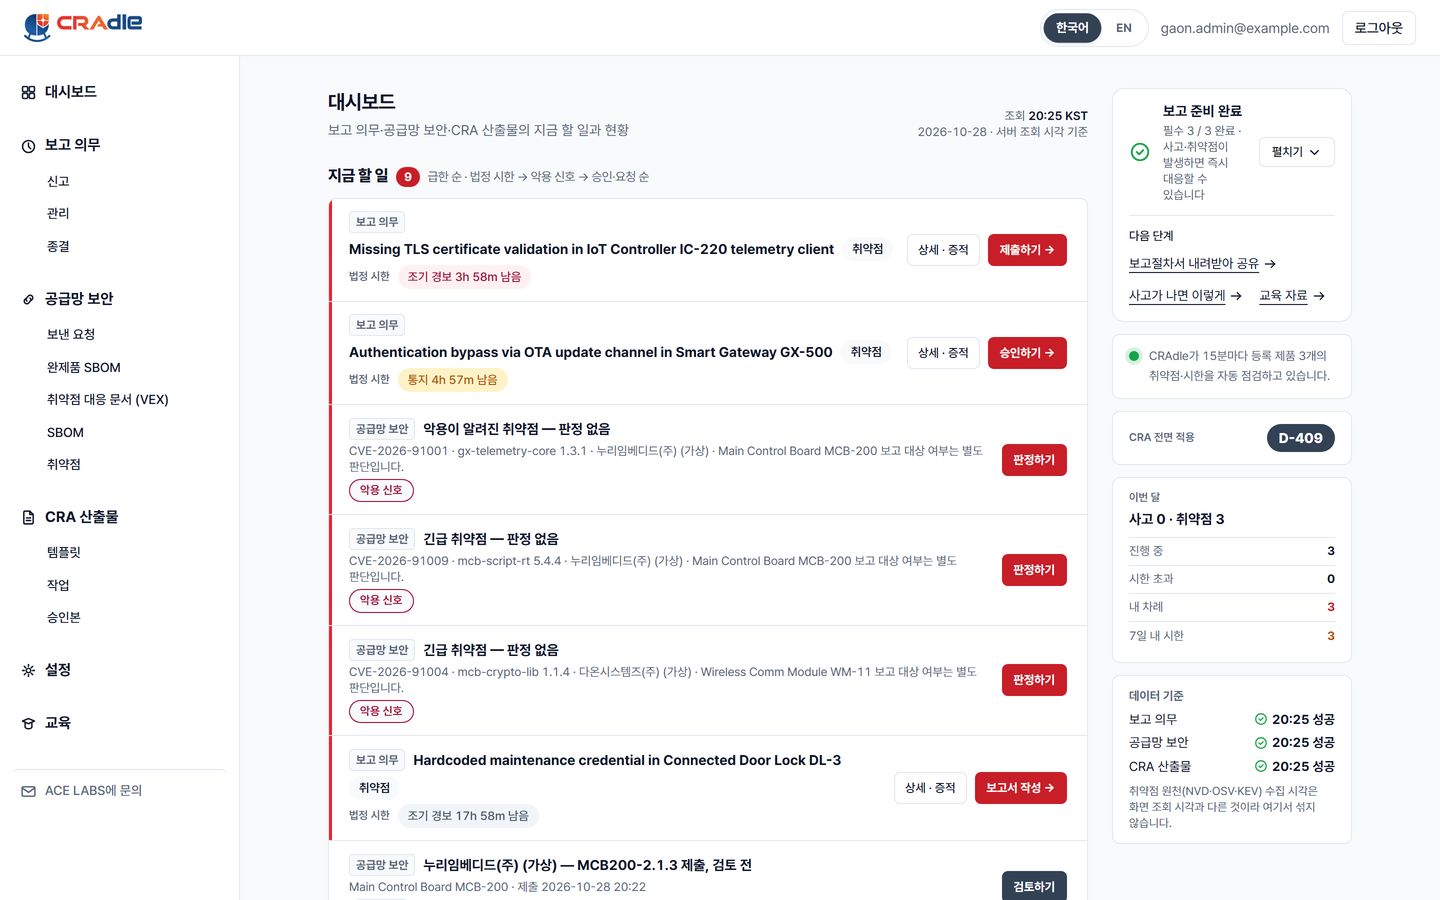
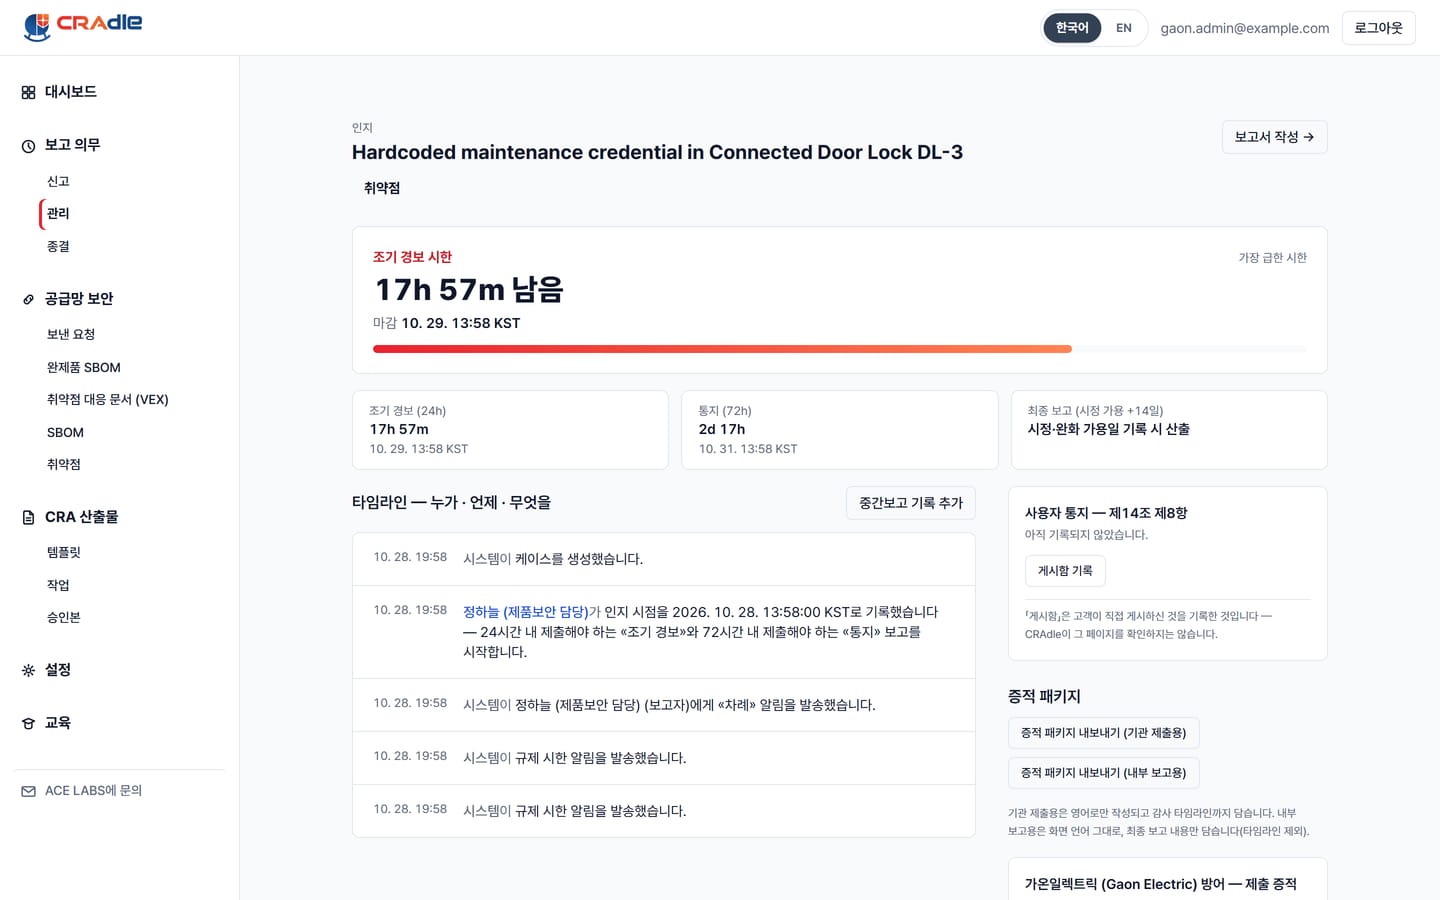
Reporting obligations
From the moment you become aware, the 24h, 72h and final deadlines are calculated, and the approval step goes to the person responsible.
Synthetic data · fictional company Supply-chain security
Request SBOMs from your suppliers and build the product SBOM from what they submit. New vulnerabilities are checked against that parts list and shown to you.
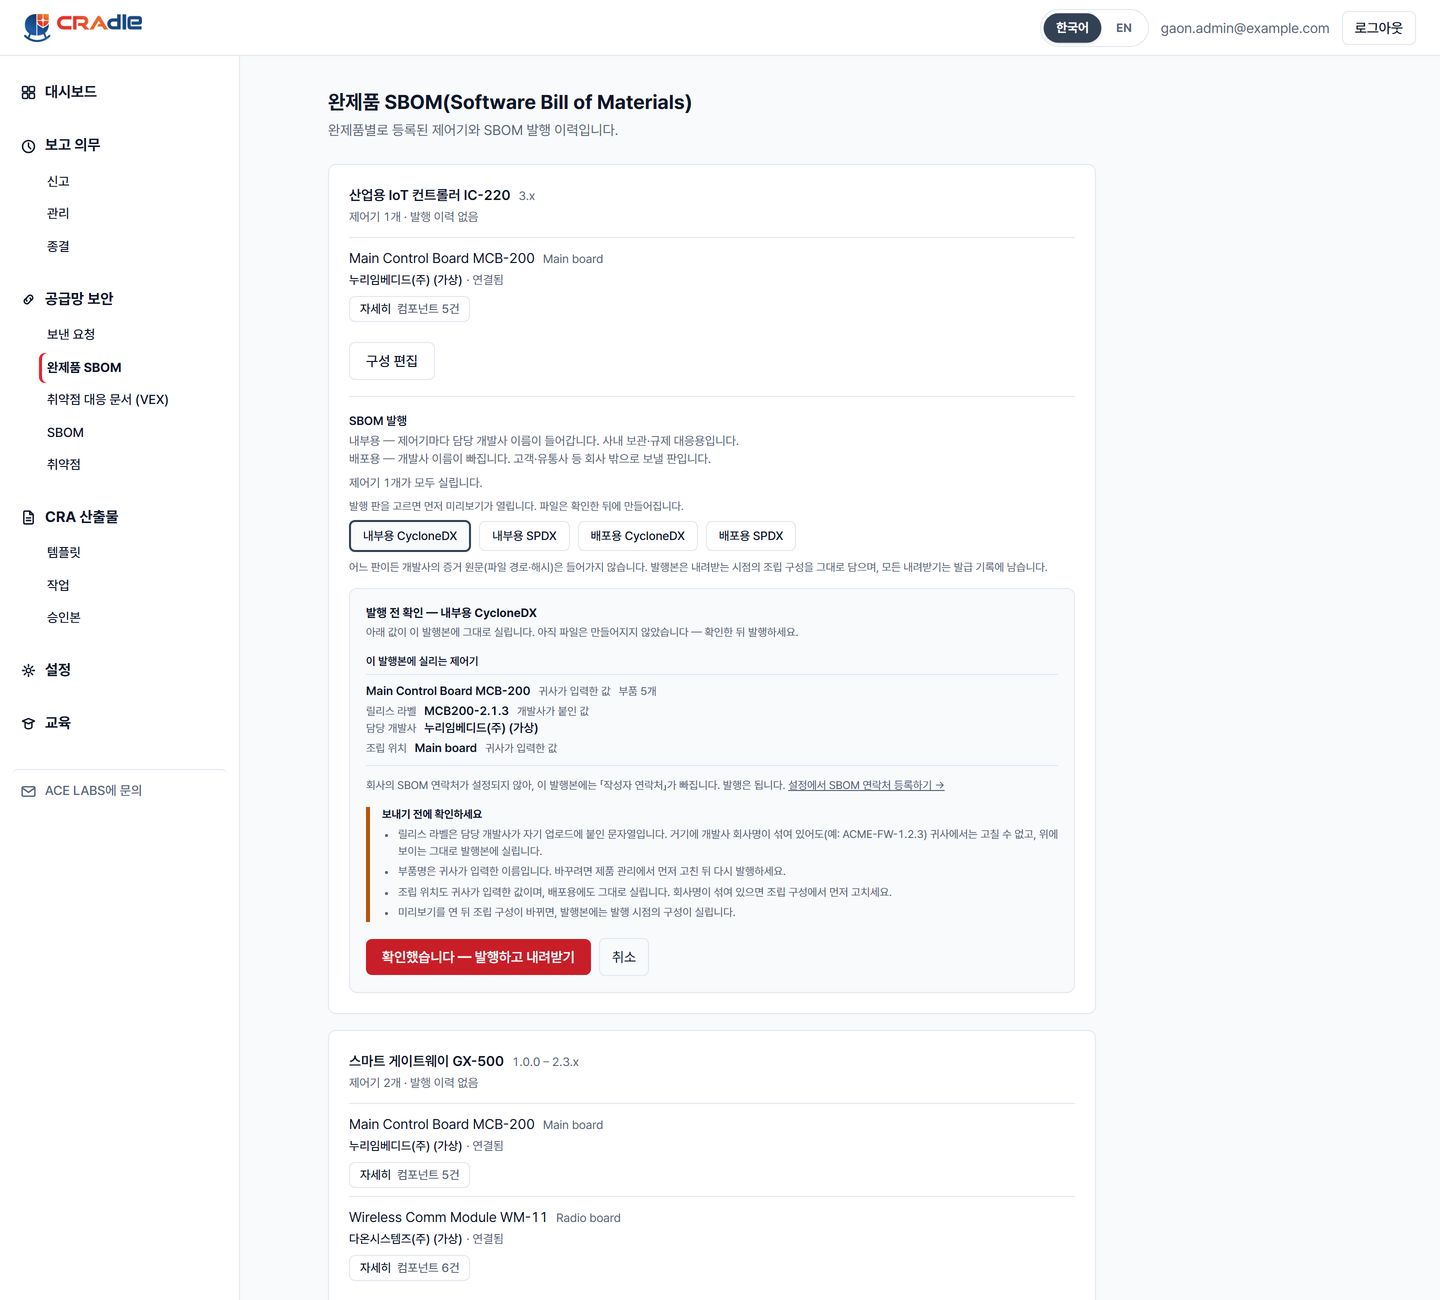
Even if a supplier provides source code, it is used only for analysis; once the analysis is finished it is destroyed and a certificate of destruction is left on record.
Synthetic data · fictional company CRA deliverables
Template → work → approved copy. Templates are prepared, and the files you upload go through sign-off and remain as approved copies.
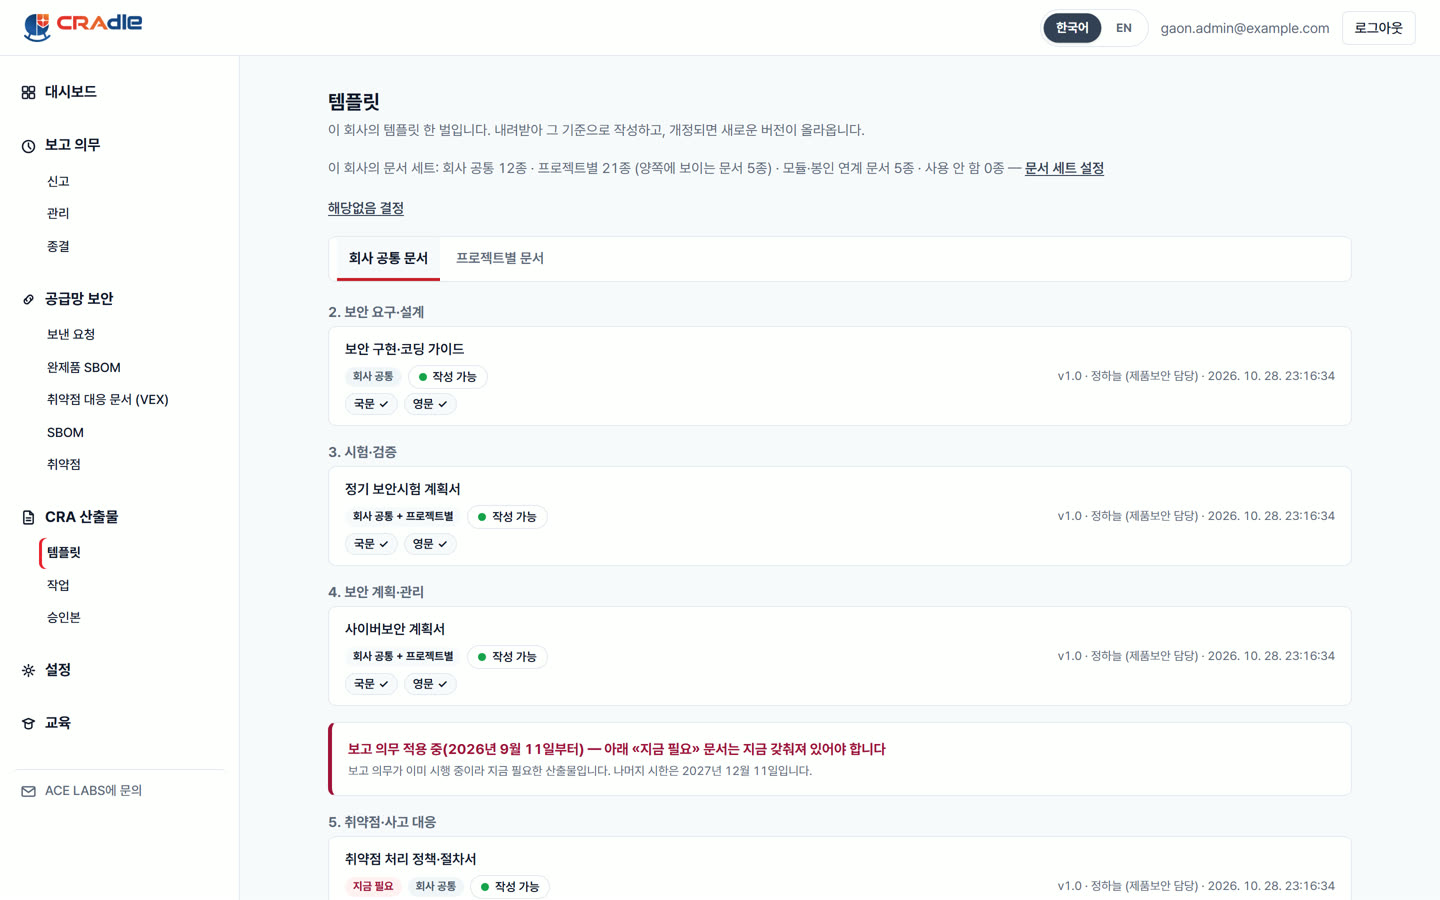
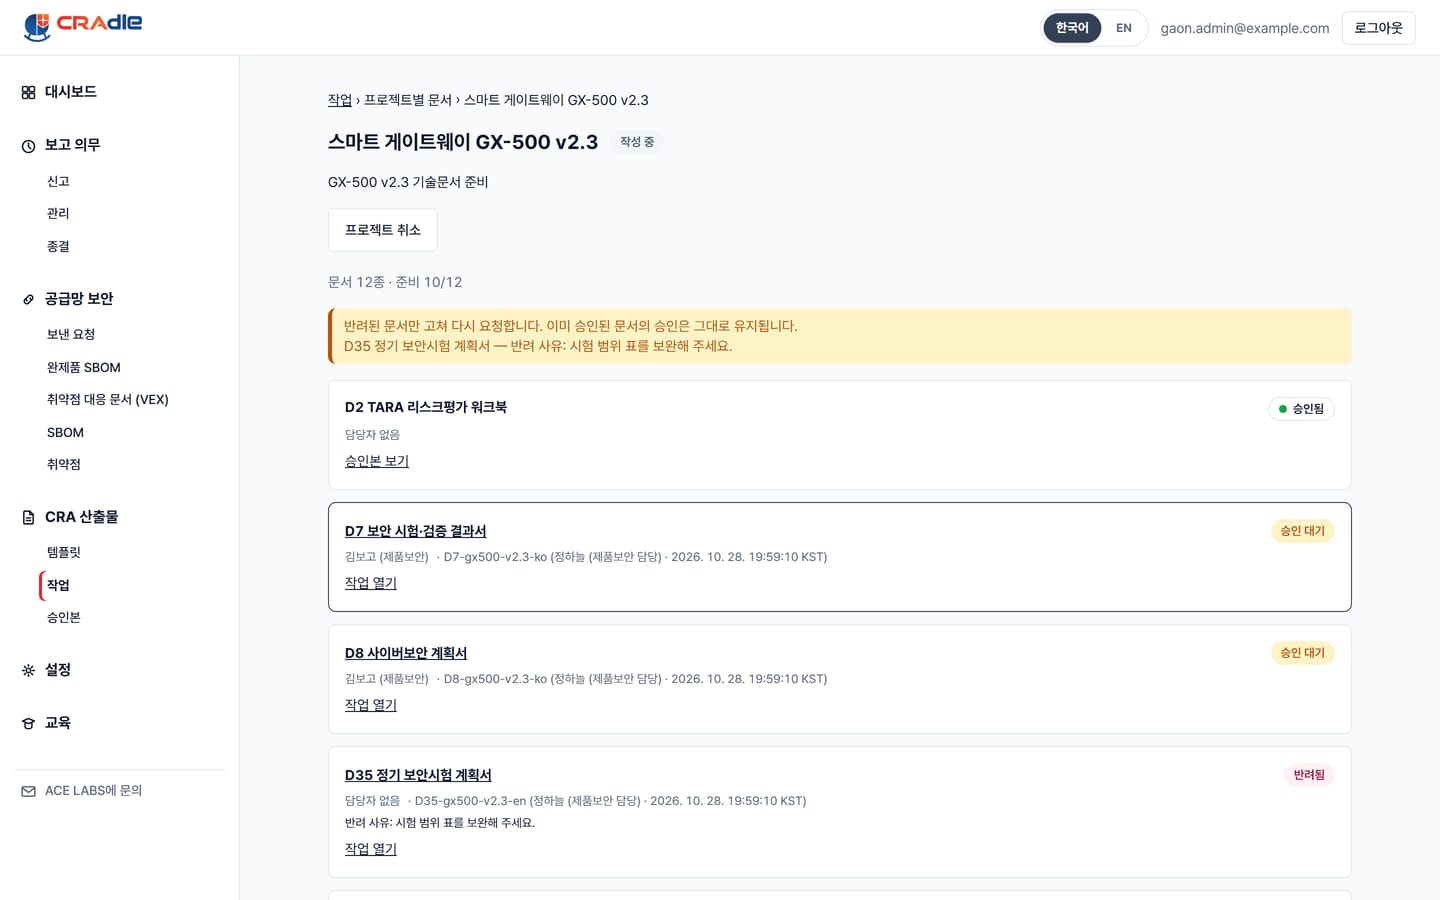
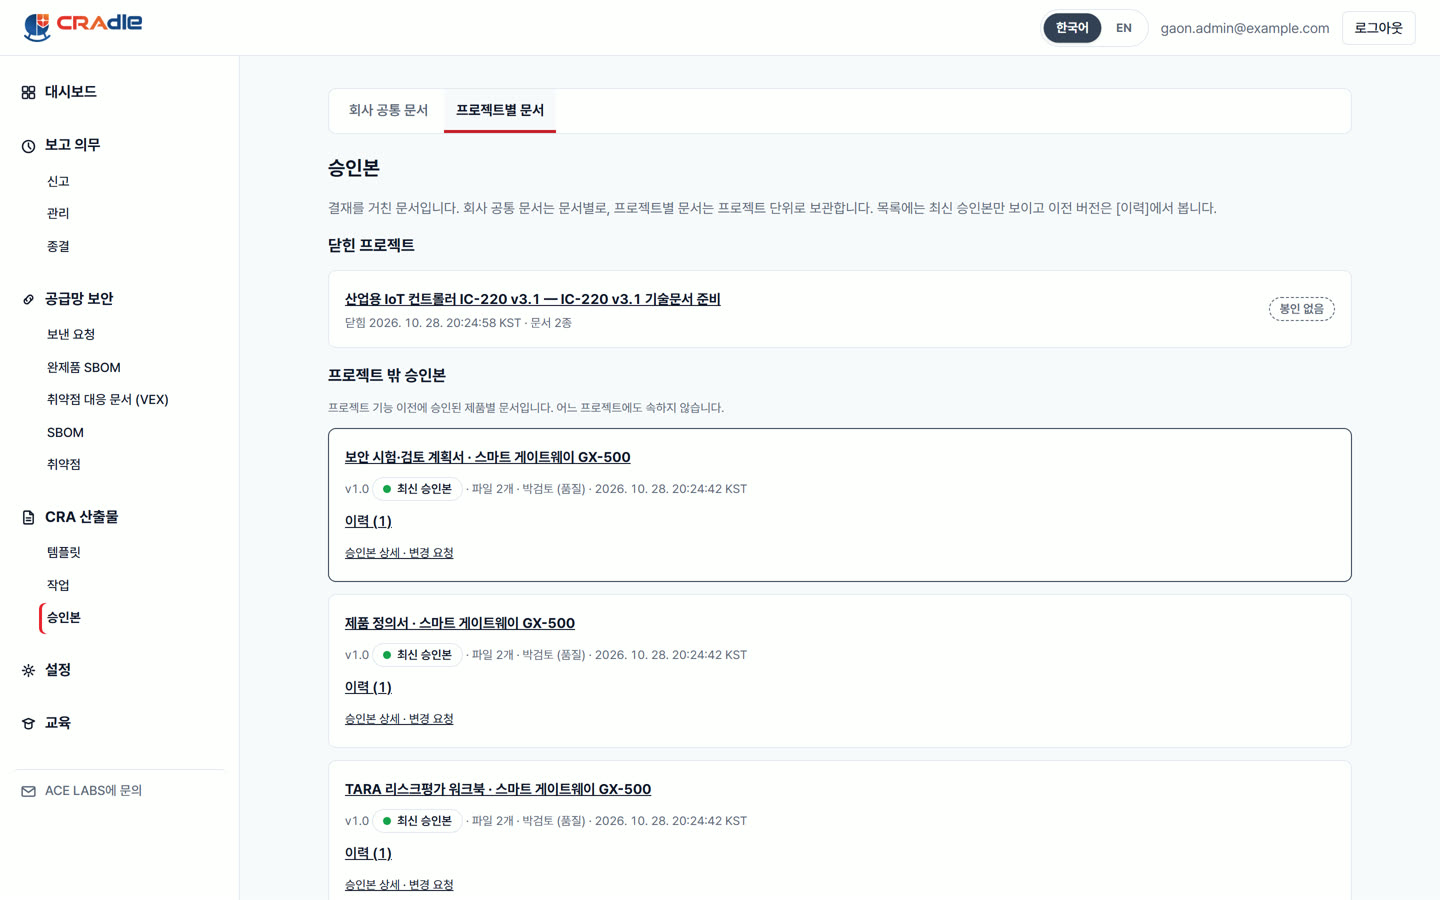
Template → work → approved copy · Synthetic data · fictional company


Three things in one place.
When you sign in, your tasks gather in one list: deadlines → exploit signals → approvals.
Synthetic data · fictional company · 16-second screen recording
Where would you like to start?
Submission and judgment stay with your company; preparation and records are CRAdle's job. Tell us where you stand and we will assess it for free.